
Communications, Media and Technology
With the development and growth in the communications, media and technology, sectors, the firm has correspondingly built a practice focused on these industries, particularly in the areas of information technology, outsourcing, e-commerce, communications, media and entertainment, to help our clients to succeed in this environment, not just by understanding the factors that drive change but by implementing practical solutions that enhance productivity, competitiveness and value. We have advised domestic and international clients in this sector, as well as clients in various other industries, including financial institutions, in their procurement of IT solutions and outsourcing. In addition to this, we advise the Government and regulators on regulatory policy in the digital economy.
Our ability to harness the relevant skills and expertise across various practices enables us to advise on a full range of issues ranging from corporate transactions such as mergers and acquisitions and joint ventures, to outsourcing and facilities management, software and hardware systems acquisitions and procurement, intellectual property rights, and the licensing, compliance and regulation issues in highly regulated sectors.
With the breadth of our experience, and our continued close working relationship with industry regulators, our team is able to provide the requisite expertise and insight into the commercial and regulatory environment of the industry.
Latest insights
Introduction
As data rapidly transforms from an organizational asset into state sovereignty, regional governments are pivoting away from outsourcing their safety to distant, centralized frameworks. Sarawak made a decisive move in late 2026 by launching the Sarawak Cybersecurity Strategy and Roadmap (SCSR) 2030, a comprehensive state-level cybersecurity framework, catering for this very objective. Driven directly by the Sarawak Multimedia Authority (SMA), this 5-year roadmap positions Sarawak as the first state in Malaysia to pioneer its own comprehensive, localized defense infrastructure.
With an ambitious objective to digitalize 100% of its public services by 2030, Sarawak is not just implementing new software, it is building a digital shield. The framework unifies 18 strategic initiatives under 5 core pillars, designed to anchor its massive pushes into green energy, advanced semiconductors, and multi-megawatt data center hubs.
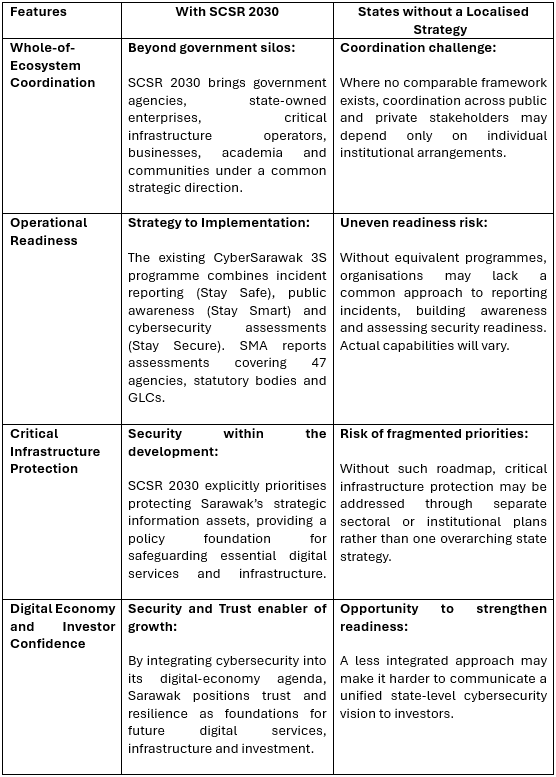
To appreciate the gravity of the SCSR 2030, we examine the features below in isolation:
Cost of Inaction: Real-World Cyber Threats
Cybersecurity vulnerabilities has proven that they bring direct, painful real-world costs, from the exposure of sensitive personal data to disruptions affecting critical infrastructure and substantial financial losses. Recent incidents across East and West Malaysia illustrate the costs from different dimensions of cyber-risk:
1. Swinburne University of Technology Sarawak — Ransomware and data theft
In August 2024,Swinburne University of Technology Sarawak was listed on the dark-web leak site of the RansomHub ransomware group, which claimed to have stolen 366 GB of data. The university subsequently confirmed that investigations had identified the theft of certain sensitive information, including passport scans, student completion letters and student applications, highlighting the risks cyberattacks pose to personal data and institutional trust.
2. Malaysia Airports Holdings Berhad — Cyberattack affecting KLIA systems
On 23 March 2025, a cyber incident affected certain computer systems at Kuala Lumpur International Airport (KLIA), operated by Malaysia Airports Holdings Berhad (MAHB). The incident prompted a full-scale investigation, with MAHB notifying the NACSA and the Civil Aviation Authority of Malaysia. The Prime Minister subsequently disclosed that hackers had demanded a USD10 million ransom, underscoring the potential stakes when cyber threats target critical transportation infrastructure.
3. Sarawak — Rising cybercrime and financial losses
Between 2024 and April 2026, Sarawak recorded 5,875 cybercrime cases involving approximately RM233.48 million in financial losses. Investment scams accounted for approximately RM132.9 million, representing around 57% of the total losses. Kuching recorded RM45.77 million in losses across 782 cases, followed by Miri with RM33.13 million across 766 cases and Sibu with RM20.40 million across 721 cases. These figures demonstrate that cybercrime is not merely a threat to institutions and infrastructure; it also inflicts substantial financial harm on individuals and communities.
4. Malaysia's ransomware threat landscape — Akira and Ransom Hub
A ransomware threat assessment published by Simply Data on 23 August 2026 identified Akira and RansomHub among the ransomware groups associated with attacks on Malaysian organisations during the first half of 2026. The report identified exposed remote-access infrastructure, including VPN appliances and Remote Desktop Protocol (RDP) endpoints, as attack vectors associated with Akira, and linked RansomHub to targets in Malaysia's financial sector. These findings reinforce the need for proactive security controls, effective threat detection and coordinated incident-response capabilities.
Taken together, these incidents illustrate the consequences of cybersecurity being an afterthought. The damage extends beyond technical disruption to personal data breaches, financial losses, threats to essential services and a loss of public trust. For businesses at the digital forefront, this presents another challenge. Innovation comes with a cost of compliance that must be factored into the business from the outset, rather than addressed only when regulatory requirements arise or an incident occurs.
In this context, the SCSR 2030 strategy prompts an important question: does introducing state-level oversight alongside existing federal regulations create an overregulated environment? Not necessarily. Instead, state-level initiatives should serve as a wake-up call for companies to view security as a core component of responsible innovation. The true test will be ensuring that state and federal frameworks align seamlessly, offering clear, balanced requirements rather than redundant paperwork that fails to improve actual protection.
We can see clearly how the SCSR 2030 has established a critical precedent. SCSR 2030 offers a framework for making cybersecurity an integral part of digital development, rather than an afterthought. The SCSR 2030 further ensures that as the state scales its digital ambitions, from localised AI hubs to smart utility grids, its sovereignty remains uncompromised. For the rest of the country, this precedent is an important one, the future lies in resilience, and it belongs to those who retain the power to protect, govern and control what they build.
This article was authored by Jonathan Lim, Managing Partner, and Laurel Lim, Senior Associate, with contributions from Nadarashnaraj Sargunaraj, Partner, and Mohamad Izahar Mohamad Izham, Partner.
This article is for general informational purposes only and does not constitute legal advice. Please contact us if you require advice on how these developments may affect your business.
The Digital Shield: Sarawak’s Building Blocks for a Fortress for its Digital Economy
One of the original promises of digital assets was simple: value moving across borders with minimal friction and full transparency. Today, Malaysia is taking steps towards that vision, developing regulated digital asset infrastructure intended to support domestic financial innovation and potentially enhance regional market integration.
Through Bank Negara Malaysia’s (BNM) Digital Asset Innovation Hub (DAIH), launched in June 2025, Malaysia has established a dedicated environment to test real-world applications. The DAIH currently emphasises testing tokenised bank deposits, while BNM’s broader strategic horizon continues to explore tokenised sukuk, stablecoins and automated supply chain finance. If this roadmap is anchored in institutional liquidity and cross-border commercial trade, Malaysia has the potential to reduce structural friction and unlock real economic value within a live banking ecosystem. The Securities Commission Malaysia (SC) is also relevant to the digital asset and tokenised capital markets framework, including tokenised sukuk. The boundary between the BNM and SC perimeters is itself an interoperability question: participants need clarity on which regulator governs each asset, activity and point in the transaction chain.
Across Asia, neighbouring jurisdictions are advancing their own tailored regulatory regimes. Singapore, for instance, has been moving beyond initial proofs of concept under Project Guardian and developing commercial digital infrastructure through Global Layer One (GL1) and settlement networks such as BLOOM, while its framework for digital payment tokens (DPTs) under the statutory Payment Services Act (PSA) and its regulatory framework for single-currency stablecoins continue to evolve. Hong Kong’s stablecoin licensing regime, which came into effect in August 2025, offers a useful comparator for how reserve-backed digital money may be supervised. Meanwhile, Taiwan has enacted a statutory framework specifically for virtual asset service providers (VASPs), although its Virtual Asset Service Act has not yet entered into force.
Individually, these domestic frameworks represent major regulatory milestones. But what happens between them when a transaction crosses a border?
Consider a scenario where a ringgit stablecoin or tokenised deposit issued under BNM’s DAIH framework interacts with an institution operating under Singapore’s PSA regime, or where a tokenised asset residing in Malaysia is settled using digital fiat originating from a foreign market. While ledger transfers execute in seconds, the underlying legal, regulatory, and institutional mechanics remain firmly bound to national borders. Critical friction points immediately surface:
- Regulatory Perimeter & Licensing: Which jurisdiction holds primary licensing authority when digital asset services, custody nodes, and smart contract execution layers span multiple borders?
- Monetary & Sanctions Reconciliation: How are foreign exchange controls, capital flow management measures, and disparate AML/CFT or sanctions screening standards reconciled between distinct payment regimes?
- Private Law & Insolvency Finality: In cross-border collateral transfers or tokenised asset defaults, which country's legal system determines property rights, choice-of-law priority and custody ring-fencing during an insolvency event? For example, if a tokenised asset held for a Malaysian investor is custodied in Singapore and the Singapore custodian becomes insolvent, does Malaysian law, Singapore law or the governing law of the tokenised asset determine whether the asset is ring-fenced from the custodian’s creditors? The answer may depend on the asset, the custody structure and the applicable conflict-of-laws rules.
Beyond Sandboxes: Building Interoperable Architecture
Sandboxes like BNM’s DAIH are essential for evaluating technical viability and informing national policy. However, a sandbox or regulatory perimeter in one market cannot, by itself, determine how a Malaysian digital asset structure legally interacts with counterparties in Singapore, Hong Kong, or beyond. That requires an overlay of legal and regulatory interoperability operating across borders.
Multilateral central bank initiatives, such as Project Mandala, led by the BIS Innovation Hub with participating central banks including BNM, MAS, Reserve Bank of Australia, Banque de France, Reserve Bank of India, Central Bank of Kuwait, Bangko Sentral ng Pilipinas takes a major step forward by exploring how regulatory parameters can be embedded directly into transaction protocols. Yet, protocol-level "compliance-by-design" is only one layer of the solution.
The surrounding legal architecture, from institutional custody agreements and master clearing documentation to the cross-border enforce ability of smart contracts must be equally interconnected. For institutional market participants, cross-border interoperability is no longer a theoretical debate. Regulatory posture is increasingly transitioning from a domestic compliance checkbox to a core pillar of regional commercial strategy.
Bridging the Gap: What Interoperability Requires
Technical interoperability is necessary but insufficient. Cross-border digital asset markets also require a legal and regulatory framework that can travel with the transaction.
- Mutual recognition or passporting between regulators, supported by clear limits and supervisory cooperation;
- Harmonised conflict-of-laws approaches, drawing where appropriate on the UNIDROIT Principles on Digital Assets and Private Law;
- Alignment of the FATF Travel Rule across corridors to support consistent AML/CFT controls;
- Standardised cross-border documentation, including master agreements and custody terms;
- ASEAN-level coordination to reduce fragmentation while preserving appropriate national safeguards.
The answer to the question posed above is yes—but only if legal interoperability is built alongside technical interoperability.
What This Means for Market Participants
For market participants, the practical agenda is immediate:
- Map the licensing touchpoints of each cross-border flow, including issuance, custody, settlement and technology services;
- Stress-test governing-law and insolvency provisions in tokenisation documentation, including the treatment of assets held through an overseas custodian;
- Align AML and sanctions screening across relevant corridors, with clear responsibility for Travel Rule information;
- Engage early with DAIH and relevant regional initiatives to test legal, regulatory and technical assumptions before scaling.
The Road Ahead
The next phase of digital assets in Asia will not merely be about perfecting domestic frameworks within individual borders; it will be about making those frameworks work together in practice. Market participants should treat legal interoperability as a design requirement: identify licensing perimeters, document governing-law and insolvency outcomes, and align AML/CFT controls before a transaction crosses a border.
Malaysia’s DAIH and regional initiatives could provide practical forums to test that approach. The jurisdictions that connect regulatory, legal and technical layers will be best placed to turn tokenisation into durable cross-border infrastructure.
This article is written by Managing Partner, Jonathan Lim and Senior Associate, Laurel Lim.
This article is for general informational purposes only and does not constitute legal advice. Please contact us if you require advice on how these developments may affect your business.
Asia Can Regulate Digital Assets, But Can It Connect Them?
The Personal Data Protection Commissioner’s Office (“JPDP”) has issued three new non-binding guidelines under the Personal Data Protection Act 2010 (“PDPA”): Data Protection by Design, Data Protection Impact Assessment, and Automated Decision-Making and Profiling. Together, they advance Malaysia’s data protection framework from reactive compliance to proactive, risk-based governance aligned with global standards.
Data Protection by Design
The DPbD Guideline requires embedding personal data protection throughout the data processing lifecycle—from design to decommissioning. It is structured around proactiveness, end-to-end protection, transparency, and user-centricity, applying these across the seven Personal Data Protection Principles. The DPbD Guideline encourages a risk-based approach tailored to each organisation’s processing activities.
Data Protection Impact Assessment
The DPIA Guideline provides guidance on identifying, assessing, and managing risks in personal data processing. A DPIA is required where processing is likely to result in high risk—determined quantitatively (more than 20,000 data subjects, or 10,000 data subjects where sensitive personal data (including financial data) is involved) or qualitatively (potential legal or significant effects on the data subject, systematic monitoring of the data subject, use of innovative technologies, denial or restriction of the data subject’s rights, tracking of the data subject’s location or behaviour, targeting of children or vulnerable individuals, and automated decision-making and profiling that present a high risk to the data subject). The Guideline prescribes the five-step “DEICA” methodology (Describe, Evaluate, Identify, Consider, Assess) and requires that DPIAs be refreshed every two years.
Automated Decision-Making and Profiling
The ADMP Guideline addresses automated systems used in personal data processing, despite the PDPA not containing specific provisions on such activities. It applies where outcomes may have legal or significant effects on data subjects (e.g., financial, employment, or service access decisions). Compliance with the Notice and Choice Principle is required, preserving the data subject’s right to withdraw consent. Notably, AI must not be the sole factor in decisions concerning data subjects, and the use of ADMP itself triggers the requirement for a DPIA.
JPDP’s power to issue guidelines
The PDPA confers on JPDP functions that include issuing guidance. Each of the three documents—the DPbD, DPIA and ADMP Guidelines—expressly records that it is issued by JPDP pursuant to subsection 48(g) of PDPA. They supplement the Act and related subsidiary instruments and are not intended to override them or to be prescriptive.
Are the Guidelines binding or legally effective?
The DPbD, DPIA and ADMP Guidelines provide guidance and promote good practice; they expressly state that they supplement and do not override the Act or subsidiary legislation. A failure to follow a Guideline does not, by itself, constitute an offence unless such non-compliance triggers a breach of the PDPA or subsidiary legislation.
Conclusion
Taken together, these guidelines form a cohesive framework reinforcing the obligations of data controllers and processors under the PDPA. The DPbD Guideline embeds privacy at the design stage, the DPIA Guideline ensures high-risk processing is rigorously assessed, and the ADMP Guideline addresses the particular challenges of automated technologies and AI.
If you have any questions or require any additional information, please contact Nadarashnaraj Sargunaraj or the partner you usually deal with in Zaid Ibrahim & Co. This alert was prepared with the assistance of Hana Wong Xin Yi, Associate in Zaid Ibrahim & Co.
This alert is for general information only and is not a substitute for legal advice.
Design. Assess. Automate—Safely: Malaysia’s New PDPA Guidelines at a Glance
As the world accelerates into the era of the Fourth Industrial Revolution, Malaysia is taking bold steps to secure its place at the forefront of digital transformation. Through the myDIGITAL initiative and the Malaysia Digital Economy Blueprint, the nation aims to evolve into a high-income, tech-driven powerhouse by 2030. Central to this vision are the development of robust data centre infrastructure and the strategic integration of artificial intelligence. In this article, our partners Cheong Yuen Wei, and Senior Associate Vivienne Caitlin Michael explore Malaysia’s digital ambitions, the opportunities that lie ahead, and the challenges of building a future-ready, inclusive digital economy in the ASEAN region.
Read the full article here.
Lexology In-Depth: Artificial Intelligence Law Malaysia
The Malaysian Communications and Multimedia Commission (“MCMC”) announced on 1 August 2024 that a new regulatory framework for Internet messaging service and social media service will come into effect on 1 January 2025.
Two Ministerial orders were gazetted on 1 August 2024 to amend the following subsidiary legislation under the Communications and Multimedia Act 1998 (“CMA”):
(i) Communications and Multimedia (Licensing) Regulations 2000; and
(ii) Communications and Multimedia (Licensing) (Exemption) Order 2000
With the amendments, service providers of “Internet messaging services” and “social media services” with more than 8 million users in Malaysia must be registered under an Applications Service Provider Class (“ASP (C)”) licence under the CMA (collectively referred to as the “Relevant Service Providers”).
“Internet messaging services” and “social media services” are defined as follows:
“Internet messaging services” means an applications service which utilizes Internet access service that enables a user to communicate any form of messages with another user.
“Social media services” means an applications service which utilizes Internet access service that enables two or more users to create, upload, share, disseminate or modify content.
MCMC has also published an Information Paper and FAQ Guide on the new licensing framework which can be accessed here.
MCMC has stated that end users of services offered by these Relevant Service Providers will not be affected by the new regulatory framework. It also reiterated that end users can expect a safer online environment, better protection against harmful content, and clearer avenues for addressing complaints and concerns.
The Relevant Service Providers are given a grace period of five months from 1 August 2024 to apply for the ASP (C) licence and comply with the relevant licensing requirements. The validity period for ASP (C) licence held by the Relevant Service Providers is one year from the registration date and the licence is required to be renewed annually.
For further enquiries, you may contact Nadarashnaraj Sargunaraj, Stanley Lee Wai Jin, Vivienne Caitlin Michael of Zaid Ibrahim & Co.
Gone Viral!!! New Licensing Framework for Internet Messaging and Social Media Platforms in Malaysia!!
This article highlights predictions from Global KPMG Legal Services leadership from around the world on how data, privacy and cyber security issues will affect the future of legal functions and legal practice. As predictions, they are not intended to guarantee any future outcomes.
Today’s legal teams are challenged by rapid technological innovations. Generative artificial intelligence (gen AI) and other new technologies are being adopted across legal functions and broader businesses at breakneck speed. While productivity is being pushed to new heights, organizations are being exposed to a new range of risks, including data privacy breaches, loss of attorney-client privilege, heightened regulatory scrutiny, ransomware and related reputational damage.
At the same time, new abilities to access, manipulate and analyze huge pools of data are compelling legal professionals, regulators and policy innovators to balance technology’s potential to drive positive social change against the dangers of exposing large swathes of sensitive personal information.
How will these trends reshape the legal functions of the future? Here are KPMG professionals’ top five predictions:
1. As gen AI becomes ever more embedded into legal function processes, legal teams will need to understand how and when to keep humans in the loop to maintain the skills needed to guard against the related risks.
The application of gen AI and other new technologies to legal work will significantly increase efficiency and productivity. These gains will grow as legal professionals get more comfortable with these powerful solutions and continue to develop more constructive ways to employ them.
Dependence on gen AI will grow apace, however, and legal teams will need to stay vigilant about the attendant risks. For example, using gen AI to inform legal advice could lead to data breaches that could affect privilege. And eventually, as gen AI subsumes ever more routine legal activities previously done by junior lawyers and paralegals, there will be fewer people in the organization with the skills to do that type of work.
Legal professionals will need to avoid the tendency to simply accept that a computer’s output is correct without questioning the reasoning behind it. They will need to develop the skills to work backwards from the output to explain how a legal conclusion was derived and independently verify whether it is accurate. Attorneys will also need to be purposeful in determining which processes are a good fit for AI and where they still need to maintain the skills to verify the legitimacy and accuracy of AI output.
2. A raft of new legislation will emerge to address a wide array of AI-related issues.
As new AI legislation is enacted, legal teams will move beyond building AI for their own use cases to advising their businesses on the AI implementation. Legal departments will need to understand all of these different rules so they can establish legal frameworks that enable the organization to innovate and use AI. This use must follow ever-evolving new laws and regulations and must proceed in a safe and trusted way.
Within these frameworks, legal teams need to set business-optimized guardrails so they can make the most of business opportunities while preventing their organizations from incurring risk.
Smart use of technology will be a key to managing these new compliance obligations. gen AI and large language model AI can ingest, decipher, summarize and automate data and regulatory and compliance rules to a much wider degree than any current technology. Legal professionals who learn how to use technology for both improving productivity and policing its use will have a distinct competitive advantage.
3. Privacy laws and approaches to open data innovation will continue to diverge. The more AI is relied on, the more the risks increase, leading to more rigorous requirements aimed at protecting personal data on one hand while enabling its use for productivity gains and positive social change on the other.
Revolutionary AI systems have enormous potential to help solve various societal problems, such as disease and vendor diversity-based discrimination. However, these systems require copious amounts of personal data to create reliable statistical conclusions, raising issues about whether the right permissions and safeguards are in place for processing that data.
Regulatory restrictions on data usage, such as data localization and data sovereignty rules, will continue to increase. However, there will be some push and pull as some jurisdictions, such as the UK, attempt to simplify those rules in order to encourage innovation, sharing of data and open data. For example, the EU Data Act aims to allow public authorities to make public data available for purposes of the wider community via a public data trust.
Legal teams are likely to increase their use of AI-enabled privacy technology to demonstrate compliance as new data protection legislation comes onstream. This technology can also make legal data analysis more efficient and ultimately help make legal decisions more consistent.
4. With gen AI’s ability to create and transform, data sources will become more opaque and harder to trace, leading to more data privacy and intellectual property disputes.
As machine learning, large language models and gen AI continue to advance and collect huge volumes of data, it will become increasingly difficult to trace and verify the sources used to train these technologies. Currently, we have seen disputes over AI’s use of copyrighted texts and artworks in generating new works. The inability to prove who “owns” a source of original data could frustrate attempts to gain intellectual property protection for AI-generated results.
Challenges in tracing data could also cause companies to run afoul of data privacy legislation by hampering their ability to comply with legislated data subject rights, such as access or erasure requests.
In-house privacy teams will need to expand their focus to streamline processes and controls and adapt to AI-related risks and regulations. Legal departments will also need to have the ability to quickly develop internal policies, procedures and controls to keep up with the pace of new usage.
5. Legal departments will be on the front lines of defending against cyber attacks and upholding organizational resilience.
Cyber security threats are likely to multiply in the future as cyber criminals become adept at using gen AI for writing ransomware, bypassing protections, spreading misinformation and other offences. Legal teams will be called on to respond to these risks on a number of fronts by:
- advising companies on consistent policies for responding to and dealing with ransomware attacks
- working with in-house technology or operational teams to implement or adopt appropriate cybersecurity technology to protect the organization’s data (in compliance with stricter data protection/cyber security laws).
- educating people across the company on cyber risks, including the guardrails needed to mitigate those risks and what red flags to watch out for
- ensuring that the people responsible for complying with data security and privacy legislation:
- have the skills to understand the sources of cyber risks and related safeguards
- maintain their human connections within the organization so they can ensure AI uses remain safe and secure.
Governments can also be expected to get involved to ensure businesses in their jurisdiction have appropriate cyber security policies and governance in place. In the near future, we are likely to see legislation enacted to mandate organizational resilience on adopting stronger cyber security technology and efficient response to cyber security breach. Legal professionals will need to help their organizations develop approaches to complying with these rules.
This article is prepared by Usman Wahid, Partner, Head of Technology Law at KPMG Law in the UK; Nadarashnaraj Sargunaraj, Head of Technology, Privacy and Cybersecurity, Zaid Ibrahim & Co. ; and Isabel Simpson, Partner, Data Protection, Technology and Telecommunications Practice Group lead, EMA.